Thursday, September 6, 2012

iLearn? AppleTV and AirPlay in the Classroom

In higher education, consumer technology is both a blessing and a curse!

The curse?
Each fall I cringe, wait and wonder what new gadget will show up in the dorms, converting wireless bandwidth into the latest gotta-have-it diversion. Faculty and staff get these gadgets too and bring them to IT asking for help in getting them to deliver the promise that was advertised.

The blessing?
New gadgets bring new opportunities to do useful things in new ways, usually at less cost.
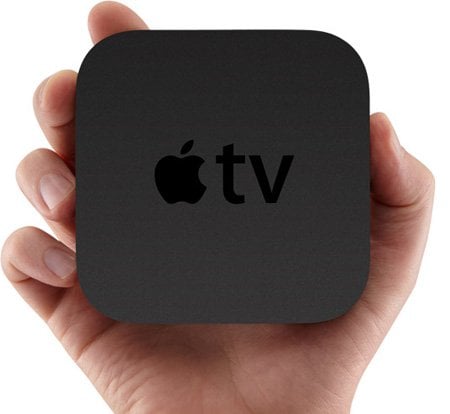
The AppleTV is an amazing example of such a gadget. At $99 it delivers a wide array of streaming media (video and audio) along with desktop mirroring (using AirPlay) to the classroom. Sure, we could use the classroom technology podium computer for desktop sharing, but this is so cool!

Actually it really is cool! Professors can now move around the classroom completely untethered from a podium. All you need is an iPad and an iTunes account (ok, maybe a NetFlix, YouTube, Hulu, ... account too) and you're GTG. 

At least, that's how the consumer technology promise goes. Of course, reality isn't quite so uncomplicated. It turns out that Apple's products
rely on the Bonjour protocol, a proprietary protocol 
that sends something called multicast packets across the network to discover other Apple devices on the same network. Colleges and universities typically use complex enterprise networks for wired and wireless connections across campus. Complex enterprise networks block multicast traffic to prevent flooding the network, and the hundreds or thousands of devices on the network, with these discovery packets. This is a big enough deal that a group of over 750 university technology administrators recently signed a petition demanding that Apple redesign their protocols to work in large enterprise networks.

To give you an example of the enterprise multicast problem, imagine coming home and yelling "Hello, is anyone home?". Now, imagine entering a room with 100 people all yelling "Hello, is anyone home?". On your small home network with a handful of devices, "shouting" works just fine, but this approach causes serious problems on a large, enterprise network, causing serious congestion over wireless networks.

Our challenge this summer was to figure out how to put an AppleTV in a classroom with a display, allowing a professor to come to class with an iPad, connect to an AppleTV over the wireless network, and use AirPlay to give a KeyNote presentation. Of course, the iPad's Remote app can also be used to play YouTube, NetFlix or Hulu video, iTunes music and a whole host of other cool content.

Well, thanks to my talented and tenacious team who figured out how to get our Cisco enterprise network to tolerate Apple's Bonjour protocol, Simpson University is rolling out AppleTVs in 5 classrooms this fall! We have professors who are excited to start using their iPads and we are excited to see if this new technology will result in more effective learning. Stay tuned!

Monday, March 26, 2012

Taking IT to the cloud

It was an epic Monday today. After a concerted two week effort, yes I said two weeks!, our university went live on Google Apps today. It's spring break this week, giving us a slight lull in the normal flow of campus life, during which we could slip this change in to the very heart of our communication infrastructure.


My IT staff rocks! Over two weeks we ran many tests, measuring an aggregate failure rate of < .04% for email, calendars and contacts. We ran directory sync against our AD to auto-provision our users. We ran Google Exchange Migration to push all emails except those from the last two weeks over to Google. Then this weekend we pushed the remaining emails, along with calendars and contacts (in separate batches) over to Google.

I have to give credit to the vast majority of our users who were patient and followed instructions pretty well. They got themselves connected with a minimum of assistance from our Help Desk. The bulk of our calls today were from people who didn't receive that last email to Outlook giving them their temporary Google password. Perhaps the biggest kudos go to one prof at our South Korea site who got himself connected with a minimum of hand holding!

The biggest obstacle? Change! It's unbelievable how many people asked if they can keep using Outlook or Entourage. In all of our communications about the Google migration we have emphasized to our users the importance of adopting the web browser as the primary user interface for Google Apps. Google is designed to be presented via the web browser. Color me so surprised that people still asked the Help Desk to hook Google up to Outlook. One professor proudly announced that he had gotten his Entourage to work with Google.

Problems encountered ... 
    1. Administrative Assistants
    We should have set up administrative assistant calendar delegations FIRST! As a result most calendar appointments for the President and VPs did not get migrated! They were very patient as we found and resolved the problem.

    2. Hidden Dependencies
    Watch out for those long forgotten dependencies like the electronic fax server and MFP dependency on a print management program that integrates with Exchange to relay outbound faxes to the fax server. Oops! BTW - this is why I have been pushing TOGAF ... it pays to have your architectural dependencies documented!


    3. Oblivious Users
    We went to a lot of trouble to prepare a migration web site with loads of getting started information, FAQs and tutorials. I can't believe how many calls we received asking about topics that we covered on our migration web site. I know, right?

    Saturday, December 10, 2011

    The Threat of Internet Anonymity

    Richard Rumelt, in his excellent blog "Strategy Land" wrote a post: "We Need to Rebuild the Internet" in which he asserts that "anonymity is a design flaw in the Internet". I agree that anonymity is a significant problem, however its causes are assignable to deeper design flaws and decisions that have implications for the future resolution of problems like spam and vulnerabilities of the Internet backbone (and thus every person, organization and state relying on the Internet) to cyberattacks.


    NAT
    In my view, the anonymity problem arises from a coupling of the Internet design assumption of identity-based trust within its most basic Internet protocols (BGP, SMTP) and the widespread adoption of Network Address Translation (NAT) in the 1990s. The 1990s witnessed explosive growth in Internet access that quickly exhausted the supply of unique Internet network addresses. Earlier in the decade, it became clear that this expansion was coming and that the Internet, if it continued using the existing addressing scheme, would be unable to support the coming expansion. The solution that was adopted is known as Network Address Translation (NAT). ISPs, since the 1990s use NAT to provide Internet addresses to their customers in a way that permits more endpoints on the Internet than there are unique Internet addresses. The price that was paid, however, was the introduction of anonymity to Internet traffic. One might think that this was an elegant solution, and in some ways it was indeed. However, the designers of NAT meant it to be a short term fix to a big and significant problem. They knew that it violated assumptions of trust and identity that are a fundamental part of the Internet's design. 


    Twenty years later, ubiquitous use of NAT across the Internet has created an environment where unscrupulous persons, willing to violate the law for financial gain or other malicious purposes, operate with impunity under the shield of anonymity. This is the ultimate cause of the spam that shows up in your inbox, the anti-virus software you run, the wasted bandwidth transporting spam and malware to your workplace only to delete it (hopefully) upon receipt, the multiple, expensive prevention systems that your workplace spends its money on instead of the valuable projects that would further your organization's objectives, and, perhaps most worrisome, the vulnerability of our communities and states to devastating cyberattacks.


    IPv6
    With change comes opportunity! IPv6 is a (sort of) new Internet addressing scheme that has the potential to solve the problem that gave rise to NAT. However, NAT is embedded in firewalls, routers and switches everywhere. The coming transition to IPv6 from IPv4 could eliminate the use of NAT on the Internet and eliminate the problem of endpoint anonymity. Eliminating anonymity will expose script kiddies and other unsophisticated cybercriminals while raising the cost of admission for those more motivated.


    Learn More
    For a detailed explanation of NAT read this 2004 article by Geoff Huston of the Centre for Advanced Internet Architectures and for more timely information about the future of the Internet, check out his blog at www.potaroo.net.


    For an introduction to trust issues with BGP read this ars technica article: "Gaping hole opened in Internet's trust-based BGP protocol".